EBOOK
One security model for your virtual machines and your containers
Running separate controls for VMs and containers leaves gaps. This checklist gives your team four concrete, actionable areas to apply consistent security controls across your whole hybrid cloud.
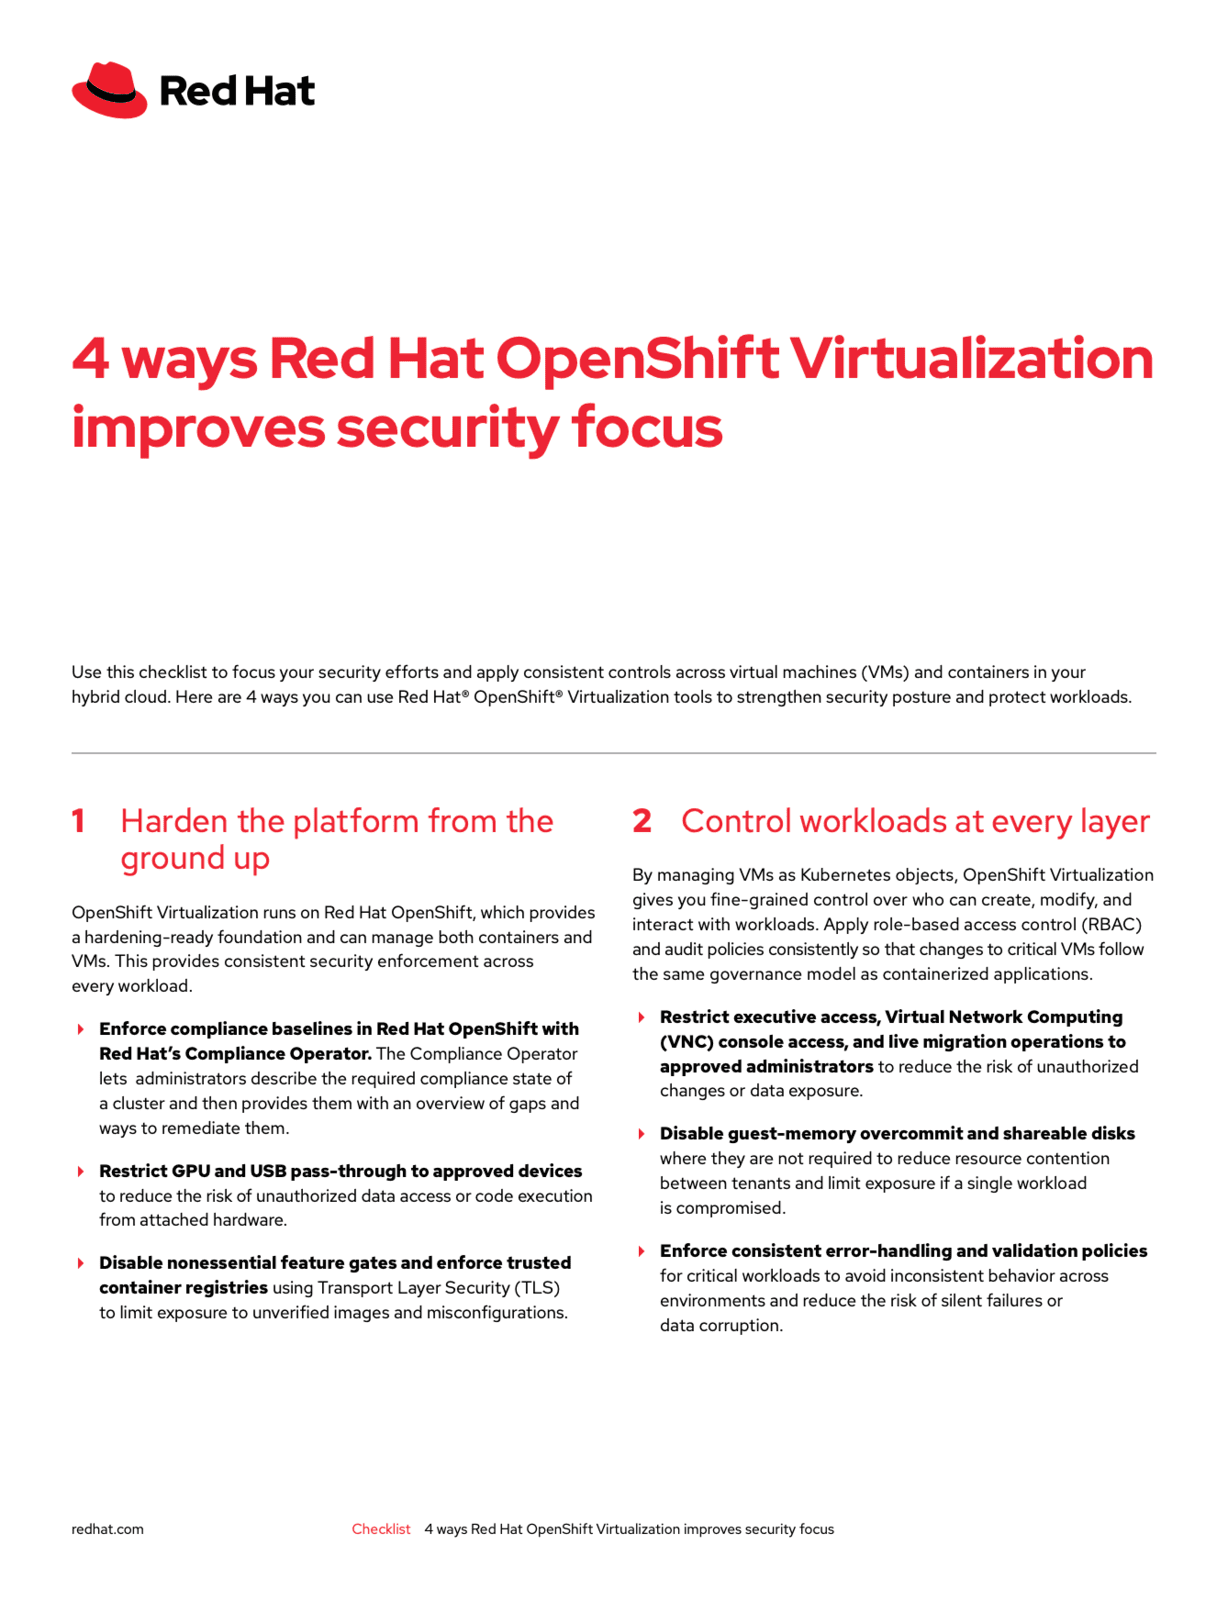
Four places to focus your security effort
FREE DOWNLOAD
4 Ways Red Hat OpenShift Virtualization Improves Security Focus
A one-page checklist your infrastructure and security teams can use directly, covering platform hardening, workload control, network segmentation, and storage integrity.
- Platform hardening controls, including the Compliance Operator
- Workload-level access control and audit policy alignment
- Network segmentation for VMs and containers alike
- Storage encryption, access, and replication policy checks
Fill in the form to start your download:
Accelerate your innovation journey